The Cost of Keeping Every Byte: Building a Defensible Data Retention Discipline
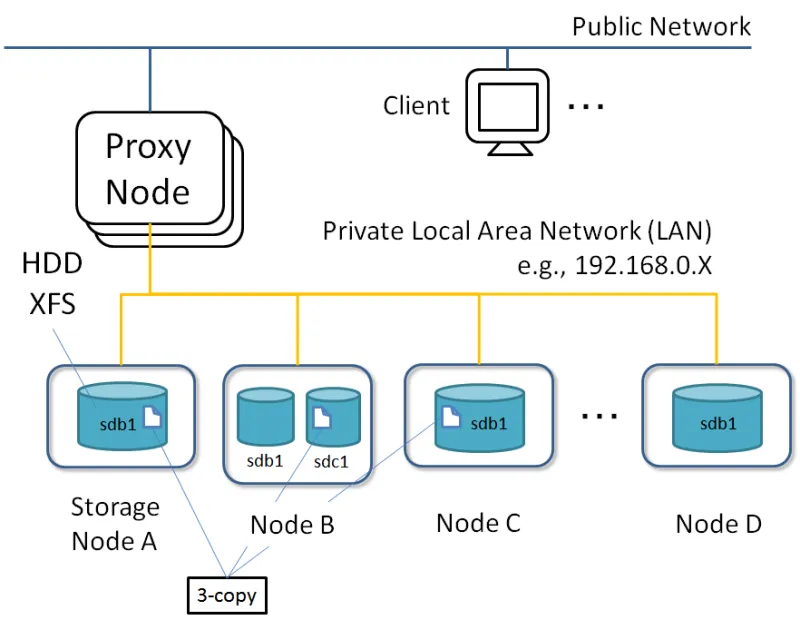
Photo: WikiTapeUser, CC BY-SA 4.0, via Wikimedia Commons
Many organizations still operate as if data storage is effectively free and retention is inherently safe. The reasoning is easy to understand: storage prices have fallen, cloud platforms scale on demand, and deleting data feels riskier than keeping it. But the business case for indefinite retention is weaker than it appears. Keeping every byte carries legal, analytical, and operational costs that compound quietly until a discovery request, a privacy inquiry, or a failed analytics project brings them into view.
This is not a argument for reckless deletion. It is an argument for defensible retention: a documented, consistent, and legally informed approach to deciding what the organization keeps, how long it keeps it, and when it disposes of it.
Why Keeping Everything Feels Safe—and Isn’t
Data retention often sits in a blind spot between legal, IT, security, and the business. Legal may assume IT is managing it. IT may assume the business owns the content. The business may assume that storage is an infrastructure concern. In the absence of clear ownership, the default is accumulation.
The problem is that data is not neutral. It can be relevant in litigation, subject to privacy obligations, useful to attackers, and costly to analyze. A large archive may feel like an asset, but it can also be a liability. The organization pays to store it, secure it, back it up, migrate it, and search it. It also pays in the form of slower analytics and lower confidence in the data that remains active.
The Three Burdens of Indefinite Retention
The first burden is legal exposure. In U.S. litigation, organizations may be required to preserve and produce relevant information. A broad data estate makes that obligation harder and more expensive to satisfy. Even when the organization has done nothing wrong, the cost of review and production can be significant. A retention policy does not eliminate discovery obligations, but it can reduce the volume of data that must be searched and reviewed.
Privacy and regulatory exposure form the second burden. U.S. state privacy laws, sector-specific rules, and contractual obligations may require organizations to limit collection, honor deletion requests, and protect sensitive information. Keeping data longer than necessary can increase the impact of a breach and complicate compliance. Retention schedules should be coordinated with legal hold obligations and privacy requirements, not treated as a purely technical cleanup exercise.
The third burden is analytical. Business intelligence depends on trusted, well-understood data. When every historical record, duplicate extract, abandoned project file, and obsolete system export is retained in the active environment, analysts spend more time filtering noise and less time generating insight. Query performance suffers. Data lineage becomes harder to trace. Users lose confidence in dashboards because the underlying data is ambiguous.
What Defensible Retention Requires
Defensible retention is not simply a deletion campaign. It is a governance discipline. At minimum, it requires a documented policy, clear ownership, consistent execution, and a process for suspending deletion when a legal hold applies. It also requires an understanding of where data lives, what it contains, and why it is being kept.
A defensible program should be able to answer basic questions. What categories of data does the organization hold? Where are they stored? Which records are subject to legal, regulatory, or contractual retention requirements? Who decides when data is no longer needed? How is deletion verified? What happens when a legal hold is issued? If these questions cannot be answered, the organization is not managing retention. It is accumulating by default.
A Practical Retention Framework
A workable framework can be built in stages. It does not require a multi-year enterprise content management program, although larger organizations may need significant effort to execute it.
-
Map the data estate. Identify the major systems, repositories, and data flows that hold business records. Include cloud applications, on-premises systems, shared drives, email, backups, and analytics environments. The goal is a practical inventory, not a perfect one.
-
Classify by record type and sensitivity. Distinguish between customer records, financial records, employee data, operational logs, project files, marketing data, and temporary working files. Classify sensitive data such as personal information, health information, financial account data, and confidential business information.
-
Identify legal and regulatory minimums. Work with legal counsel to determine which records must be retained and for how long. Retention requirements vary by industry, state, and contract. A retention schedule should reflect those obligations without treating every record as if it were subject to the longest possible period.
-
Assign business value. For each category, ask what business purpose the data serves after the active period. Some data is needed for customer service, warranty, audit, or historical analysis. Some is kept only because no one has decided to delete it. Distinguish between those cases.
-
Set retention periods and disposition actions. Define how long each category remains in active use, when it moves to archive, and when it becomes eligible for deletion. Build in exceptions for legal holds, investigations, and open disputes. The schedule should be specific enough to execute and flexible enough to accommodate legitimate needs.
-
Separate archive from active analytics. Archiving is not the same as keeping data in the production environment. Move infrequently accessed records to a controlled archive with appropriate access, search, and retention controls. Keep active analytics environments focused on data that is current, relevant, and well-documented.
-
Automate disposition where possible. Manual deletion programs tend to stall. Configure retention rules in systems where the technology supports it. Track exceptions. Verify that deletions propagate to backups and derived datasets according to policy and legal requirements.
-
Audit and improve. Review the retention schedule annually or when business conditions change. Monitor deletion volumes, legal hold activity, storage growth, and user exceptions. Use those signals to refine the policy.
Archiving Is Not the Same as Keeping Everything
A common objection to retention discipline is that the business may need old data someday. That concern is valid, but it does not justify keeping every version of every record in every system. A well-designed archive can preserve important records while removing them from active analytics and operational environments. The key is to define what must be preserved, for how long, and under what access controls.
Backups deserve separate attention. Organizations should understand how retention rules apply to backup copies and disaster recovery environments. Deletion from a primary system may not immediately remove data from backups. Legal and IT teams should align on a defensible approach that balances recovery needs with retention obligations.
The Analytics Benefit
Retention discipline is often framed as a risk and compliance exercise. It is also a business intelligence opportunity. Smaller, cleaner datasets are easier to document, query, and trust. Analysts spend less time reconciling duplicates and obsolete records. Data stewards can focus on the fields and records that matter. Leaders get faster answers from systems that reflect the current business rather than a sediment of every past process.
For SKBee Solutions, the message is not that data should be deleted casually. It is that retention should be intentional. A defensible policy helps the organization keep what it needs, protect what is sensitive, and dispose of what no longer serves a purpose. That is better for legal risk, better for operations, and better for the intelligence the business relies on.